Nemcon Systems Offer Website Development and online E-Commerce Store. Social Media Marketing & Social Media Post Designs.

FOLLOW US ON:

Get in touch!

"Have questions or ready to elevate your skills? Reach out to us today and let's shape your future together."

Umar Block Allama Iqbal Town

Red Team & Blue Team 20+ Years Excellence in Lahore 4.9/5 (680+ Reviews)

Master Diploma in Cybersecurity, Ethical Hacking & Network Defense

Master Ethical Hacking, Network Penetration Testing, and Cyber Defense with 100% Hands-on Virtual Labs & Real-World Attack Scenarios. Simulate offensive exploits in Kali Linux & Metasploit, and defend enterprise infrastructures with Wazuh SIEM, pfSense, and Snort.

3-4 Months 120+ Lab Hours
Offensive & Defensive Red & Blue Team Range
25+ Tools Kali, Metasploit, SIEM
CEH / Security+ Global Exam Alignment
Direct Admission Desk: 0321 46 33 555 • Umar Block, Allama Iqbal Town, Lahore
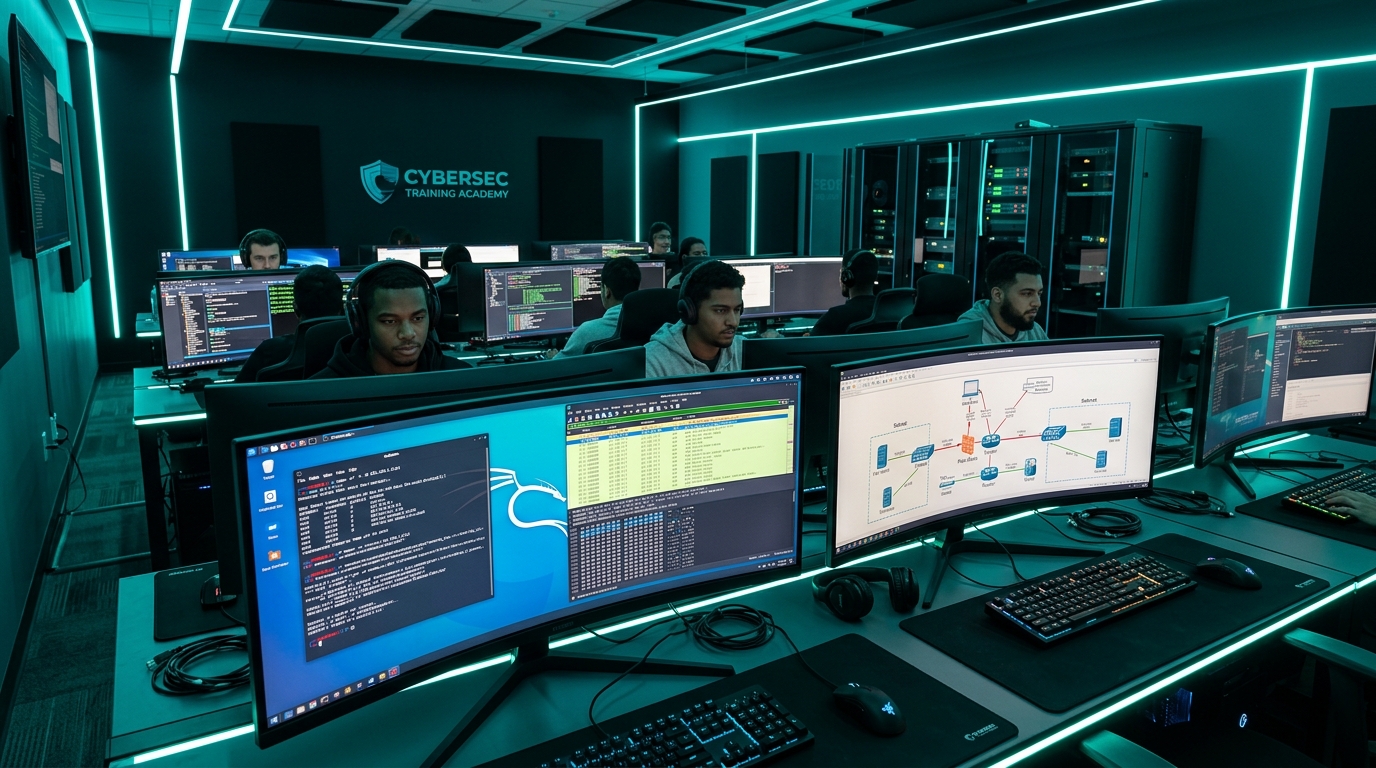
Student performing penetration testing in Kali Linux virtual lab at Nemcon Systems Lahore
Live Cyber Range Training 100% Isolated Virtual Labs • Zero Slide Lectures
INDUSTRY-READY SECURITY SPECIALIZATION

Offensive Penetration Testing & Enterprise Blue Team Operations

Train under senior industry consultants. Build the hands-on technical competencies demanded by corporate banks, telecoms, software houses, and multinational security operations centers (SOCs).

Hands-on Range Onsite Lahore & Online Live
6 Core Security Pillars

Comprehensive Offensive & Defensive Specialization Pillars

Master the full spectrum of cyber warfare—from active network reconnaissance and system exploitation to web application testing and SOC SIEM telemetry.

Pillar 01

Cybersecurity Fundamentals & Network Defense

Establish unshakeable fundamentals in the CIA Triad (Confidentiality, Integrity, Availability), defense-in-depth, security policies, OSI Layer security (L2–L7 vulnerabilities), and port security. Configure stateful inspection firewalls and IDS/IPS sensors to thwart unauthorized intrusions.

  • CIA Triad & Threat Vector Analysis
  • OSI 7-Layer Protocol Vulnerabilities
  • Stateful Firewalls (pfSense Configuration)
  • Snort & Suricata IDS/IPS Rules
Pillar 02

Reconnaissance & Ethical Hacking Essentials

Conduct full-spectrum footprinting and passive intelligence gathering (OSINT). Master network reconnaissance with Nmap scripts, banner grabbing, vulnerability scanning with Tenable Nessus, and target attack surface mapping.

  • OSINT Framework & Shodan Profiling
  • Maltego & theHarvester Recon
  • Advanced Nmap Scanning & NSE Scripting
  • Enterprise Vulnerability Auditing with Nessus
Pillar 03

System Penetration Testing & Exploitation

Execute real offensive exploits against Windows Server and Linux machines in our Metasploitable lab. Weaponize Metasploit, deploy Meterpreter shells, bypass antivirus, crack passwords with Hashcat, and escalate local privileges.

  • Metasploit Framework (MSF) Exploitation
  • MSFVenom Custom Payload Crafting
  • Windows & Linux Privilege Escalation (PrivEsc)
  • GPU Password Cracking with Hashcat & John
Pillar 04

Web Application Security (OWASP Top 10)

Audit and exploit critical web application flaws. Intercept and tamper HTTP traffic using Burp Suite. Discover SQL Injection, Cross-Site Scripting (XSS), CSRF, and Broken Access Control to excel in web pentesting and bug bounty hunting.

  • Burp Suite Professional Intercept & Repeater
  • SQL Injection (Manual & SQLmap Automation)
  • Cross-Site Scripting (XSS: Stored & Reflected)
  • IDOR, CSRF, and File Upload Bypasses
Pillar 05

Wireless & Network Attacks Analysis

Understand wireless security protocols (WPA2/WPA3), 4-way handshake capture, and deauthentication analysis. Execute Man-in-the-Middle (MitM) attacks, ARP poisoning, and dissect malicious packet captures using Wireshark.

  • 802.11 Frame Dissection & Monitor Mode
  • Aircrack-ng 4-Way Handshake Cracking
  • Man-in-the-Middle (MitM) & ARP Poisoning
  • Deep Packet Inspection via Wireshark
Pillar 06

SOC Operations & Defensive Security

Step into the role of a Tier 1 SOC Analyst. Collect, normalize, and analyze system event logs with Wazuh SIEM. Master the NIST Incident Response lifecycle, hunt for indicators of compromise (IoCs), and preserve forensic evidence.

  • Wazuh SIEM Server & Endpoint Telemetry
  • SOC Tier 1 Alert Triage & Playbooks
  • MITRE ATT&CK Framework Mapping
  • Incident Handling & Memory Forensics Basics
Cyber Range Showcase

Zero Theory. 100% Terminal Muscle Memory.

Real offensive cyber skills cannot be developed on PowerPoint slides. At Nemcon Systems Lahore, every trainee operates their own isolated virtual attack range with target servers and defensive sensors.

Student performing penetration testing in Kali Linux virtual lab at Nemcon Systems Lahore
Offensive Security Cyber Range

Red Team Attack Range: Kali Linux & Metasploit Exploitation

Execute real exploits against Metasploitable 2 & 3, vulnerable Windows Domain Controllers, and OWASP web targets inside an isolated virtual sandbox.

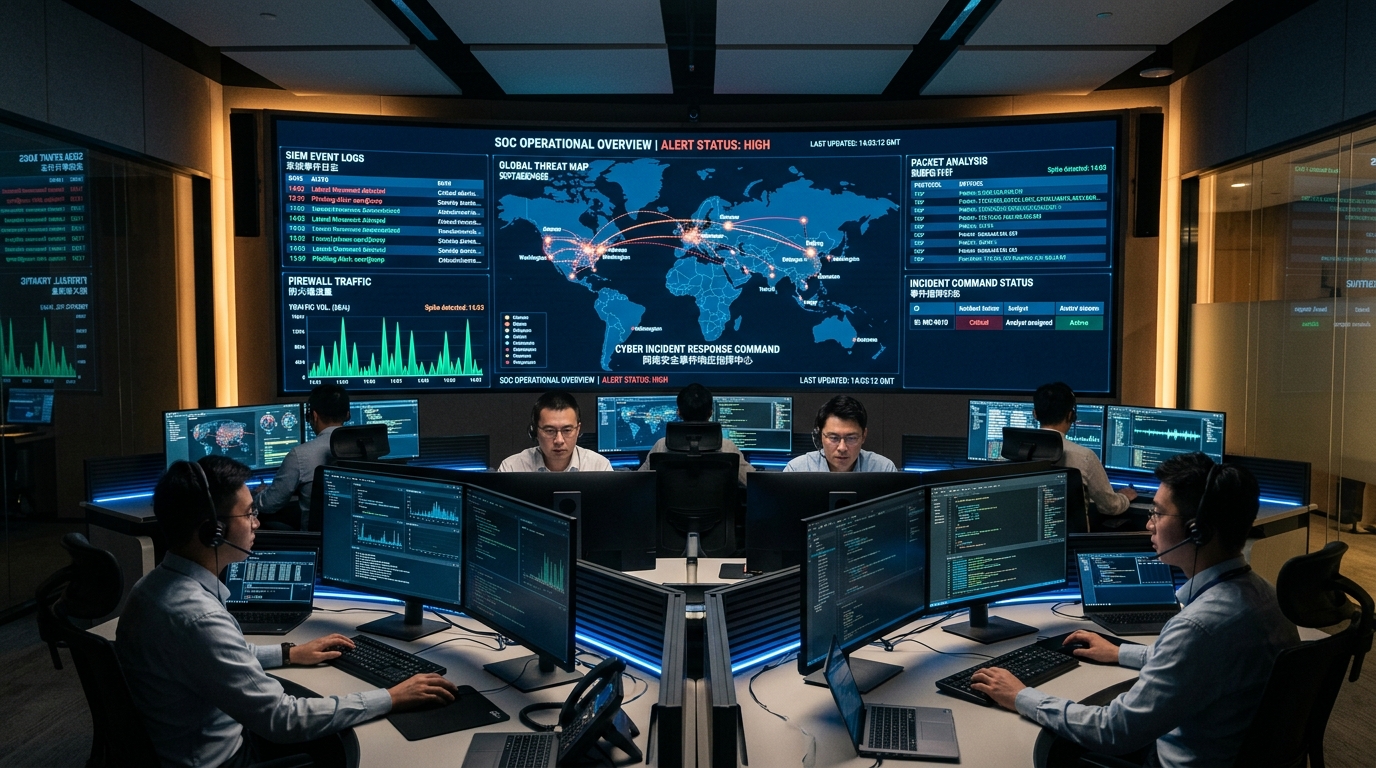
Cyber defense operations center showing SIEM log analysis and network threat monitoring at Nemcon Systems
Blue Team SOC Defense Center

SOC Operations Lab: Wazuh SIEM Threat Telemetry & Mitigation

Monitor live network telemetry, triage attack alarms, correlate log events in Wazuh SIEM dashboards, and craft automated blocking rules in pfSense firewalls.

Isolated Virtual Range

Safe, segregated VMware ESXi & VirtualBox networks to launch exploits without legal risks.

Real Target Systems

Practice against Active Directory, Linux servers, DVWA, and unpatched SMB targets.

Command-Line Fluency

Master terminal execution across Nmap, Metasploit, Hashcat, Burp, and Wireshark.

24-Hour CTF Tournament

Compete in Capture The Flag challenges to capture root flags and prove industry readiness.

Step-by-Step Roadmap

Practical 8-Module Curriculum Breakdown

Engineered across 4 progressive training phases to transition you from foundational networking to offensive penetration tester and SOC analyst.

M01

Networking Essentials for Hackers & Defensive Security

Phase 1: Foundations • TCP/IP, Ports, Protocols & Architecture

  • OSI 7-Layer & TCP/IP Stack deep-dive for security analysts
  • IPv4 Subnetting, CIDR notation & network segmentation
  • Protocol dissection: DNS, DHCP, ARP, HTTP/S, SSH, FTP, SMB
  • TCP Three-Way Handshake & TCP flags (SYN, ACK, FIN, RST)
  • Switch port security, VLAN segmentation, and NAT routing
  • Hands-on Lab: Wireshark packet capture & protocol inspection
M02

Linux Terminal Fluency & Lab Environment Setup

Phase 1: Foundations • Kali Linux & Virtualization Setup

  • Installing VMware Workstation & VirtualBox virtual lab ranges
  • Deploying Kali Linux 2026 & Parrot Security OS
  • Linux file hierarchy, permissions (chmod, chown), processes
  • Grep, sed, awk, piping, and bash scripting automation
  • Networking commands (ip, ifconfig, netstat, ss, traceroute)
  • Hands-on Lab: Building automated recon bash scripts
M03

Reconnaissance, OSINT & Vulnerability Scanning

Phase 2: Offensive Pentesting • Information Gathering & Scanning

  • Passive Footprinting: Shodan, Censys, Google Dorking
  • OSINT Framework, WHOIS, DNS reconnaissance & zone transfers
  • Active scanning: Nmap (SYN scan, UDP scan, NSE scripting engine)
  • Enterprise Vulnerability Assessment using Tenable Nessus
  • Vulnerability prioritization with CVSS scoring
  • Hands-on Lab: Complete target reconnaissance audit report
M04

System Penetration Testing & Metasploit Exploitation

Phase 2: Offensive Pentesting • Red Team Exploitation

  • Metasploit Framework architecture (exploits, payloads, aux)
  • MSFVenom custom shellcode & payload generation
  • Remote exploitation of Windows SMB (EternalBlue / MS17-010)
  • Linux & Windows Local Privilege Escalation (PrivEsc)
  • Password cracking with Hashcat, John the Ripper, Hydra
  • Hands-on Lab: Metasploitable 2 root compromise lab
M05

Web Application Security & OWASP Top 10

Phase 3: Web & Wireless • Bug Bounty & Application Pentest

  • Burp Suite Pro/Community proxy configuration & Repeater
  • SQL Injection (In-band, Error-based, Blind) & SQLmap automation
  • Cross-Site Scripting (Reflected, Stored, DOM-based XSS)
  • Broken Access Control & IDOR (Insecure Direct Object Reference)
  • CSRF tokens, file upload bypass, SSRF attacks
  • Hands-on Lab: Full exploitation of OWASP Juice Shop & DVWA
M06

Wireless Security & Man-in-the-Middle (MitM) Attacks

Phase 3: Web & Wireless • Network Interception

  • 802.11 Wi-Fi frames: Management, Control & Data frames
  • Aircrack-ng: Monitor mode, deauth attack & 4-way handshake capture
  • WPA2/WPA3 password cracking with Hashcat GPU dictionaries
  • ARP Poisoning and spoofing with Bettercap / Ettercap
  • DNS Spoofing and SSL Stripping conceptual mitigations
  • Hands-on Lab: Capturing network traffic in Wireshark and decrypting credentials
M07

Defensive Security, Firewalls & Intrusion Prevention

Phase 4: Blue Team & SOC • Enterprise Hardening

  • Defense-in-depth security architecture & zero trust models
  • Deploying and configuring pfSense open-source firewall
  • Writing custom Snort & Suricata IDS/IPS detection rules
  • Host-based firewall hardening (iptables, Windows Defender Firewall)
  • Active Directory security: Group Policy Objects (GPOs) hardening
  • Hands-on Lab: Building an impenetrable perimeter firewall lab
M08

SOC Operations, Wazuh SIEM & Capstone CTF Challenge

Phase 4: Blue Team & SOC • Real-Time Defense Project

  • SOC Analyst Tier 1 workflows & alert triage checklists
  • Deploying Wazuh SIEM server, agents, and dashboards
  • MITRE ATT&CK framework mapping & threat hunting
  • NIST Incident Response Lifecycle: Preparation to Lessons Learned
  • Digital forensics basics: RAM dump & disk image triage (Autopsy)
  • Capstone: Final 24-Hour Attack & Defense CTF Tournament

Want the Complete 120-Hour Module Breakdown?

Download the detailed week-by-week lab schedule, virtual range topologies, and tool installation handbook.

Career Pathways

International Certifications & High-Growth Job Roles

Our training directly aligns with global vendor benchmarks so you can sit for international credentials and step into high-paying cybersecurity careers.

EC-Council v13 Ready

CEH (Certified Ethical Hacker)

Covers reconnaissance, network scanning, malware threats, sniffing, social engineering, and web application attack vectors.

100% Core Objectives Covered
CompTIA SY0-701

CompTIA Security+

Universal enterprise standard covering threats, attacks, vulnerabilities, architecture, risk management, and security operations.

Foundation for Global Security Jobs
Cisco 200-201 CBROPS

Cisco CyberOps Associate

Mastery of security concepts, common network attacks, security monitoring, host-based analysis, and security incident response.

Ideal for SOC Tier 1 Roles
OffSec / Practical Hands-on

Bug Bounty & OSCP Pathway

Develops the hands-on methodology needed to discover zero-day bugs on HackerOne/Bugcrowd and prepares for grueling 24-hr offensive exams.

Real CTF Exploitation Skills

4 In-Demand Career Roles You Can Pursue:

High demand across software houses, telecom, banking, and overseas cyber firms.

Red Team Track

Junior Penetration Tester

Conduct authorized simulated cyberattacks on corporate networks and applications to uncover critical security loopholes before black-hat hackers do.

Estimated Salary: PKR 80K - 160K+ / Mo
Blue Team Track

SOC Analyst (Tier 1)

Monitor 24/7 security event streams in SIEM dashboards, investigate anomalous indicators of compromise (IoCs), and mitigate live security incidents.

Estimated Salary: PKR 85K - 170K+ / Mo
Infrastructure

Network Security Engineer

Deploy and configure enterprise next-gen firewalls, VPN tunnels, intrusion prevention sensors, and ensure compliance across the organizational network.

Estimated Salary: PKR 90K - 180K+ / Mo
Global Freelance

Vulnerability / Bug Hunter

Hunt web vulnerabilities on public and private bug bounty platforms (HackerOne, Bugcrowd) or provide independent penetration testing consultancies.

Earnings: $500 - $3,000+ / Bounty
Frequently Asked Questions

Got Questions About Cybersecurity & Ethical Hacking?

Clear answers to help you start your career in offensive penetration testing and cyber defense with Nemcon Systems in Lahore.

What are the prerequisites for this course? Do I need prior coding knowledge?

No prior coding or computer science degree is required to enroll. Our instructors start from basic computer networking (IP addresses, ports, protocols) and fundamental Linux command-line operations before introducing advanced penetration testing tools. Anyone with basic computer curiosity and logical thinking can succeed in this diploma.

Is Ethical Hacking legal in Pakistan, and what code of ethics is taught?

Ethical Hacking is 100% legal when done with explicit written consent and authorization. We strictly teach white-hat methodologies compliant with the Prevention of Electronic Crimes Act (PECA 2016) of Pakistan and international ethical guidelines. All attack simulations and exploits are conducted inside our secure, isolated virtual lab ranges.

What laptop or hardware specifications do I need for the virtual attack labs?

To run virtual machines simultaneously (Kali Linux, Windows Target, and Metasploitable), we recommend a laptop or desktop with an Intel Core i5 (8th Generation or newer) or AMD Ryzen 5 CPU, 16 GB RAM (minimum 8 GB will work with fewer concurrent VMs), and at least 100 GB of free SSD space. At our Lahore campus, we also provide fully configured lab workstations for onsite students.

How long is the course duration and what batch schedules are available?

The program is an intensive 3 to 4 months diploma comprising 120+ hours of combined instructor-led training and virtual lab execution. We offer flexible batch schedules including morning, evening, and special Saturday/Sunday weekend batches specifically tailored for university students and working professionals.

Which global security certifications does this Master Diploma prepare me for?

The curriculum maps directly into the core exam domains of Certified Ethical Hacker (CEH v13) by EC-Council, CompTIA Security+ (SY0-701), and Cisco Certified CyberOps Associate (200-201). In addition to official course credentials from Nemcon Systems, you receive full exam readiness mentoring and sample practice question banks.

What career prospects and freelance Bug Bounty opportunities exist after graduation?

Cybersecurity is among the highest-paid domains worldwide with zero percent unemployment. Our graduates enter roles such as Junior Penetration Tester, SOC Analyst (Tier 1), Information Security Officer, and Network Security Administrator. Furthermore, we mentor students on how to legally report vulnerabilities on HackerOne and Bugcrowd to earn US dollar bounties from home.

Limited Seats (Max 12 Students per Batch)

Take Command of Your Career in Cybersecurity & Ethical Hacking

Stop watching tutorials. Start testing real vulnerabilities and defending enterprise systems under senior industry guidance at Nemcon Systems, Lahore.

Official Completion Diploma 100% Practical Virtual Labs Campus: Umar Block, Allama Iqbal Town, Lahore Serving Pakistan Since 2006