
Ethical Hacking Course in Lahore
& Cybersecurity Certification
Master offensive penetration testing, Kali Linux cyber weapons, and defensive network security with 100% Hands-on Virtual Labs & Real Attack Topologies. Prepare for the global Certified Ethical Hacker (CEH v13) certification under senior industry mentorship at Nemcon Systems.
Why Master Ethical Hacking at Nemcon Systems?
Learn how cybercriminals think so you can defeat them. Develop deep technical muscle memory through real offensive attack simulations and enterprise vulnerability remediation.
Zero Slide Theory
Forget endless PowerPoint lectures. From day one, you boot up Kali Linux, scan targets, exploit unpatched services, and build custom exploit payloads on real command-line terminals.
100% Practical Virtual SandboxOffensive & Defensive Balance
Learn both sides of cyber combat: launch attacks like a Red Teamer (Metasploit, Burp Suite), and harden systems like a Blue Teamer with firewalls, IDS sensors, and log analysis.
Red Team + Blue Team SkillsBug Bounty & Freelance Scope
Learn how to ethically hunt vulnerabilities on platforms like HackerOne and Bugcrowd. Earn high-paying dollar rewards from the comfort of your home in Lahore.
Earn Bounties GloballyComplete 8-Module Step-by-Step Syllabus
Every single module is mapped to industry job requirements and international CEH v13 exam domains.
M01 Introduction to Ethical Hacking, Footprinting & Reconnaissance
Module 1 • OSINT, Threat Vectors, Legal Guidelines & Information Gathering
Introduction to Ethical Hacking, Footprinting & Reconnaissance
Module 1 • OSINT, Threat Vectors, Legal Guidelines & Information Gathering
Learn the core ethics, cyber legalities (PECA 2016), and master passive reconnaissance to uncover a target's hidden digital perimeter before launching any attack.
- Ethical Hacking methodology, scope of work, and PECA 2016 laws
- Passive Reconnaissance: Google Hacking Database (GHDB) & Dorking
- Open Source Intelligence (OSINT) with theHarvester & Maltego
- WHOIS lookup, DNS interrogation & zone transfer enumeration
- Shodan & Censys device scanning for exposed servers & webcams
- Hands-on Lab: Compiling a complete reconnaissance audit dossier
M02 Network Scanning & Vulnerability Assessment
Module 2 • Nmap Scripting Engine, Wireshark & Nessus Scanning
Network Scanning & Vulnerability Assessment
Module 2 • Nmap Scripting Engine, Wireshark & Nessus Scanning
Discover live hosts, identify open ports, probe listening services, and scan for unpatched software flaws using industry-standard vulnerability scanners.
- TCP Three-Way Handshake analysis & TCP flag states (SYN, ACK, FIN, RST)
- Nmap scan techniques (SYN Stealth, UDP, Null, FIN, Xmas scans)
- Nmap Scripting Engine (NSE) for automated vulnerability detection
- Banner grabbing, OS fingerprinting, and service version enumeration
- Enterprise vulnerability auditing with Tenable Nessus & OpenVAS
- Hands-on Lab: Performing an automated network vulnerability audit
M03 System Hacking, Exploitation & Privilege Escalation
Module 3 • Metasploit Framework, Meterpreter, Password Cracking & PrivEsc
System Hacking, Exploitation & Privilege Escalation
Module 3 • Metasploit Framework, Meterpreter, Password Cracking & PrivEsc
Gain unauthorized root/administrator access on vulnerable Windows Server and Linux machines, crack password hashes, and establish persistent backdoors.
- Metasploit Framework architecture (exploits, payloads, encoders, aux)
- Meterpreter payload execution, process migration & keylogging
- Exploiting remote vulnerabilities (SMB EternalBlue MS17-010, RDP BlueKeep)
- Local Privilege Escalation (PrivEsc) on Linux (SUID) and Windows (Token abuse)
- Password hash extraction (SAM / /etc/shadow) and cracking with Hashcat & John
- Hands-on Lab: Root compromise of Metasploitable 2 & 3 targets
M04 Web Application Security & OWASP Top 10
Module 4 • Burp Suite Proxy, SQL Injection, XSS, CSRF & IDOR Exploits
Web Application Security & OWASP Top 10
Module 4 • Burp Suite Proxy, SQL Injection, XSS, CSRF & IDOR Exploits
Learn how modern web applications are compromised. Intercept HTTP requests, bypass authentication barriers, and exploit critical application layer flaws.
- Burp Suite Professional setup, Intercept Proxy, Repeater, and Intruder
- OWASP Top 10 vulnerabilities (2021/2026 latest standard)
- SQL Injection (SQLi): Error-based, Union-based, Blind & SQLmap automation
- Cross-Site Scripting (Reflected, Stored, DOM XSS) & session hijacking
- Insecure Direct Object References (IDOR) & Broken Access Control
- Hands-on Lab: Full exploitation of OWASP Juice Shop & DVWA
M05 Wireless Network & IoT Security
Module 5 • Wi-Fi 4-Way Handshake Cracking, Deauth Attacks & MitM
Wireless Network & IoT Security
Module 5 • Wi-Fi 4-Way Handshake Cracking, Deauth Attacks & MitM
Analyze over-the-air 802.11 radio signals, intercept wireless traffic, capture encryption handshakes, and execute Man-in-the-Middle network manipulations.
- 802.11 Wi-Fi frames: Management, Control & Data frame dissection
- Setting wireless adapters into Monitor Mode with airmon-ng
- Deauthentication attacks and capturing WPA/WPA2 4-Way Handshakes
- Cracking WPA2-PSK pre-shared keys using Hashcat GPU wordlists
- ARP Poisoning & Man-in-the-Middle (MitM) attacks with Bettercap
- Hands-on Lab: Capturing cleartext credentials over wireless LAN
M06 Cryptography, Evading IDS, Firewalls & Honeypots
Module 6 • Ciphers, Hashing, Payload Obfuscation & Evasion Tactics
Cryptography, Evading IDS, Firewalls & Honeypots
Module 6 • Ciphers, Hashing, Payload Obfuscation & Evasion Tactics
Understand encryption algorithms, secure communication channels, and techniques used by advanced penetration testers to bypass IDS/IPS and next-gen firewalls.
- Symmetric vs Asymmetric encryption (AES, RSA, ECC) & SSL/TLS
- Cryptographic hashing (MD5, SHA-256) & digital signatures
- Understanding Intrusion Detection Systems (Snort, Suricata rules)
- Evasion techniques: Packet fragmentation, proxy chains & Tor routing
- Payload encoding and obfuscation to bypass signature detection
- Hands-on Lab: Evading pfSense firewall and Snort IDS alerts
M07 Cloud Security & Penetration Testing Fundamentals
Module 7 • AWS & Azure Shared Security Model, S3 Buckets & Cloud IAM
Cloud Security & Penetration Testing Fundamentals
Module 7 • AWS & Azure Shared Security Model, S3 Buckets & Cloud IAM
Examine cloud architecture security, cloud identity and access management (IAM) misconfigurations, and how modern penetration testers assess cloud infrastructure.
- Cloud Shared Responsibility Model (IaaS, PaaS, SaaS)
- Identifying public AWS S3 bucket leaks and blob storage exposures
- Cloud IAM privilege escalation and insecure access keys
- Serverless and containerized security basics (Docker / Kubernetes)
- Cloud auditing tools: ScoutSuite and Prowler
- Hands-on Lab: Auditing a misconfigured cloud tenant for privilege leaks
M08 Final Capstone Project: Real-World Penetration Testing Report
Module 8 • End-to-End Black-Box Hack, CVSS Scoring & Executive Reporting
Final Capstone Project: Real-World Penetration Testing Report
Module 8 • End-to-End Black-Box Hack, CVSS Scoring & Executive Reporting
Synthesize everything you have learned in a live 24-hour virtual target attack. Conduct reconnaissance, breach the target network, escalate privileges, and compile an executive remediation report.
- Full black-box penetration testing scenario on an enterprise subnet
- Pivot through multi-tiered internal network subnets
- Vulnerability categorization and scoring using Common Vulnerability Scoring System (CVSS v3.1)
- Drafting an Executive Summary for C-level leadership
- Writing Technical Proof-of-Concept (PoC) steps and remediation roadmaps
- Final Capstone Defense: Oral presentation and report review
Need the Complete 8-Module Syllabus PDF?
Download the detailed week-by-week lab schedule, virtual range topologies, and tool installation handbook.
25+ Industry Cyber Weapons & Lab Environment
Practice on real tools used by ethical hackers, government penetration testers, and Fortune 500 security analysts.
Red Team Attack Range: Kali Linux & Metasploit Exploitation
Execute exploits against Metasploitable 2 & 3, vulnerable Windows Active Directory domains, and OWASP web targets inside an isolated virtual sandbox.
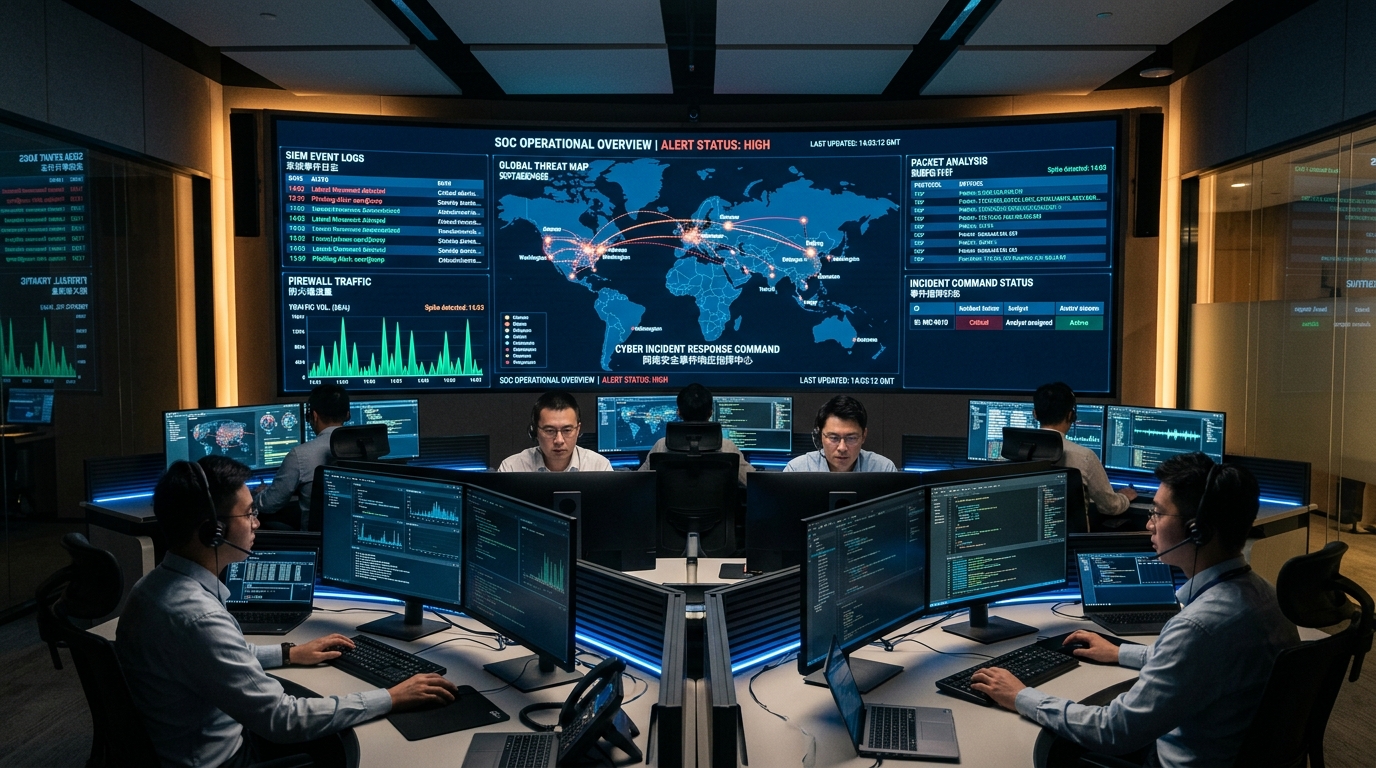
Defensive Countermeasures: Wazuh SIEM & Snort Telemetry
Understand what defenders see. Observe real attack telemetry in Wazuh SIEM dashboards, dissect packet captures in Wireshark, and write mitigation firewall rules in pfSense.
Tools & Frameworks Mastered During Training:
Who Should Enroll & Prerequisites
Designed for aspiring cybersecurity professionals, university graduates, and IT administrators looking to transition into ethical hacking.
- Computer Science & IT Students
Build real practical experience outside academic theory and graduate with job-ready penetration testing portfolios.
- Network & System Administrators
Upgrade your skillset from regular administration to high-paying network security and cyber defense engineering.
- Aspiring Bug Bounty Hunters
Learn structured web application security auditing methodology to earn US dollar bounties on HackerOne and Bugcrowd.
- IT Support & Career Switchers
Transition into the zero-unemployment domain of information security with step-by-step mentor guidance.
We teach networking fundamentals, basic Linux commands, and security concepts from the ground up.
Recommended Laptop Specs for Labs:
- Processor: Intel Core i5 (8th Gen+) or AMD Ryzen 5
- RAM: 16 GB recommended (minimum 8 GB)
- Storage: 100 GB free SSD storage for virtual machines
- Operating System: Windows 10/11, macOS, or Linux host
Onsite students in Lahore also get access to dedicated high-performance lab workstations at our campus.
Common Questions About Ethical Hacking in Lahore
Find answers to the most common queries regarding course fees, batch schedules, certifications, and career scope.
What is the fee and duration of the Ethical Hacking course in Lahore?
The course runs for 8 to 10 weeks comprising 100+ hours of combined instructor-led lectures and hands-on virtual lab execution. Nemcon Systems offers affordable fee structures with flexible student installment options. To receive the current discounted fee voucher, chat with our admissions team on WhatsApp at 0321 46 33 555.
Do I need a coding or computer science background to join this course?
No prior programming or computer science degree is required. Our instructors start from basic computer networking (IP addresses, subnets, ports, OSI layers) and fundamental Linux terminal navigation before advancing to penetration testing tools. Anyone with curiosity and basic computer literacy can succeed.
Is an official certification provided upon course completion?
Yes. Upon completing all laboratory assignments and the capstone penetration testing project, students receive an official, industry-recognized Certificate in Ethical Hacking & Penetration Testing from Nemcon Systems (serving Pakistan since 2006). The syllabus also thoroughly prepares you for the international Certified Ethical Hacker (CEH v13) certification.
Are the lab sessions 100% hands-on and practical?
Yes! 100% of our training is lab-driven. Every student configures their own isolated virtual attack range using Kali Linux, Metasploitable targets, Windows Active Directory servers, and deliberately vulnerable web applications without touching theoretical slides.
Is ethical hacking legal in Pakistan, and what laws are covered?
Ethical hacking is 100% legal when performed with written authorization and clear rules of engagement. We strictly educate students on ethical boundaries and compliance with Pakistan's Prevention of Electronic Crimes Act (PECA 2016) and global cyber laws. All attack simulations occur strictly within our isolated virtual labs.
What job opportunities and freelance bug bounty prospects exist after graduation?
Graduates qualify for high-demand IT security roles such as Junior Penetration Tester, SOC Analyst (Tier 1), Information Security Officer, and Vulnerability Analyst in local banks, software houses, and telecom operators. Furthermore, we mentor students on how to legally report vulnerabilities on HackerOne and Bugcrowd to earn US dollar bounties from home.
Ready to Become a Certified Ethical Hacker?
Register at Nemcon Systems Lahore today. Master offensive Kali Linux tools, web application security, and network penetration testing with 100% hands-on virtual lab access.